AI Security · AppSec · Product Security
I work on the parts of security that help teams ship with confidence.
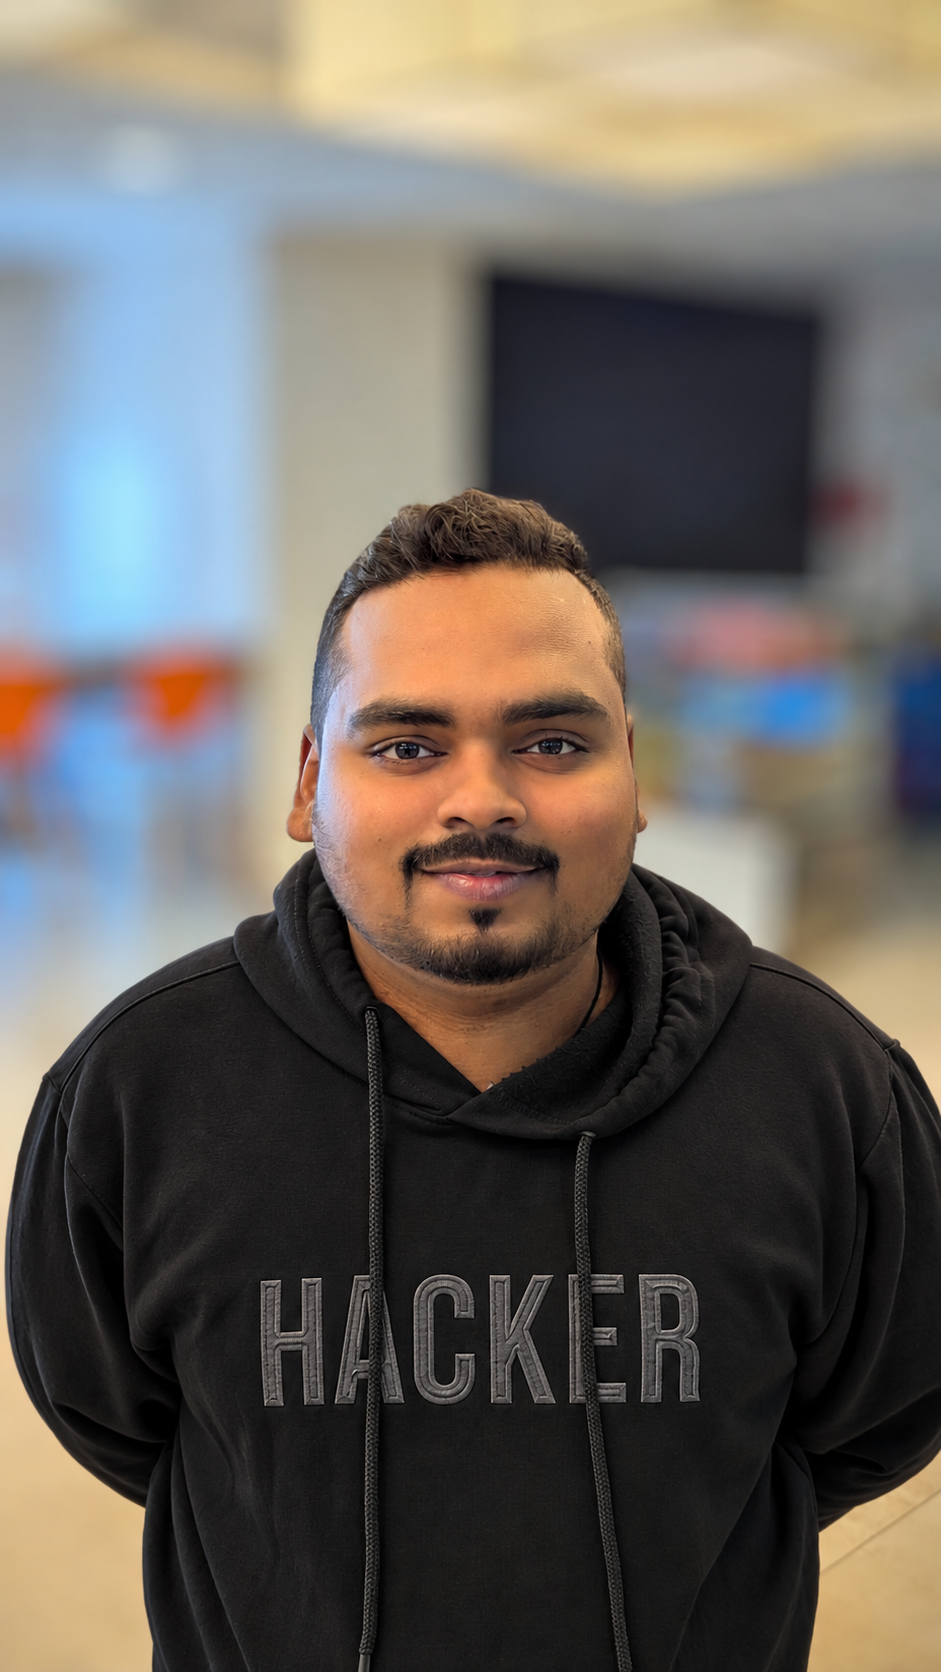
Product Security Engineer focused on application security and AI security. My work spans secure SDLC practices, security testing, threat modeling, and practical conversations with engineering teams. In my free time, I work on AI security research and build open-source security tools.
Open to work
Open to full-time and contract opportunities in AppSec, product security, and AI/LLM security — based in Hyderabad or fully remote.
About
I work across the secure SDLC of a fintech SaaS company, helping teams understand and address security risk in a practical way. This includes SAST and DAST triage, software composition analysis, secrets detection, threat modeling, and vendor security review. I try to keep the focus on what is genuinely exploitable and what an engineer can do next.
Earlier in my career, I worked on full-scope application security penetration testing (VAPT) across web, mobile, network, and API surfaces. That experience shaped how I approach security findings today: clear evidence, fair severity, and remediation guidance that the receiving team can use.
Outside of work, I do independent bug bounty research on YesWeHack under the handle mrclown. I have been active there since 2023.
Where the work concentrates
Experience
June 2024 — Present
Fintech SaaS company · Hyderabad, India
Oct 2023 — June 2024
Fintech SaaS company · Hyderabad, India
Skills
I do bug bounty research on YesWeHack and have been active there since 2023.
202
points earned
2023
active since
Certifications
CNSP
CCSP-AWS
eWPTX
Community
null Hyderabad
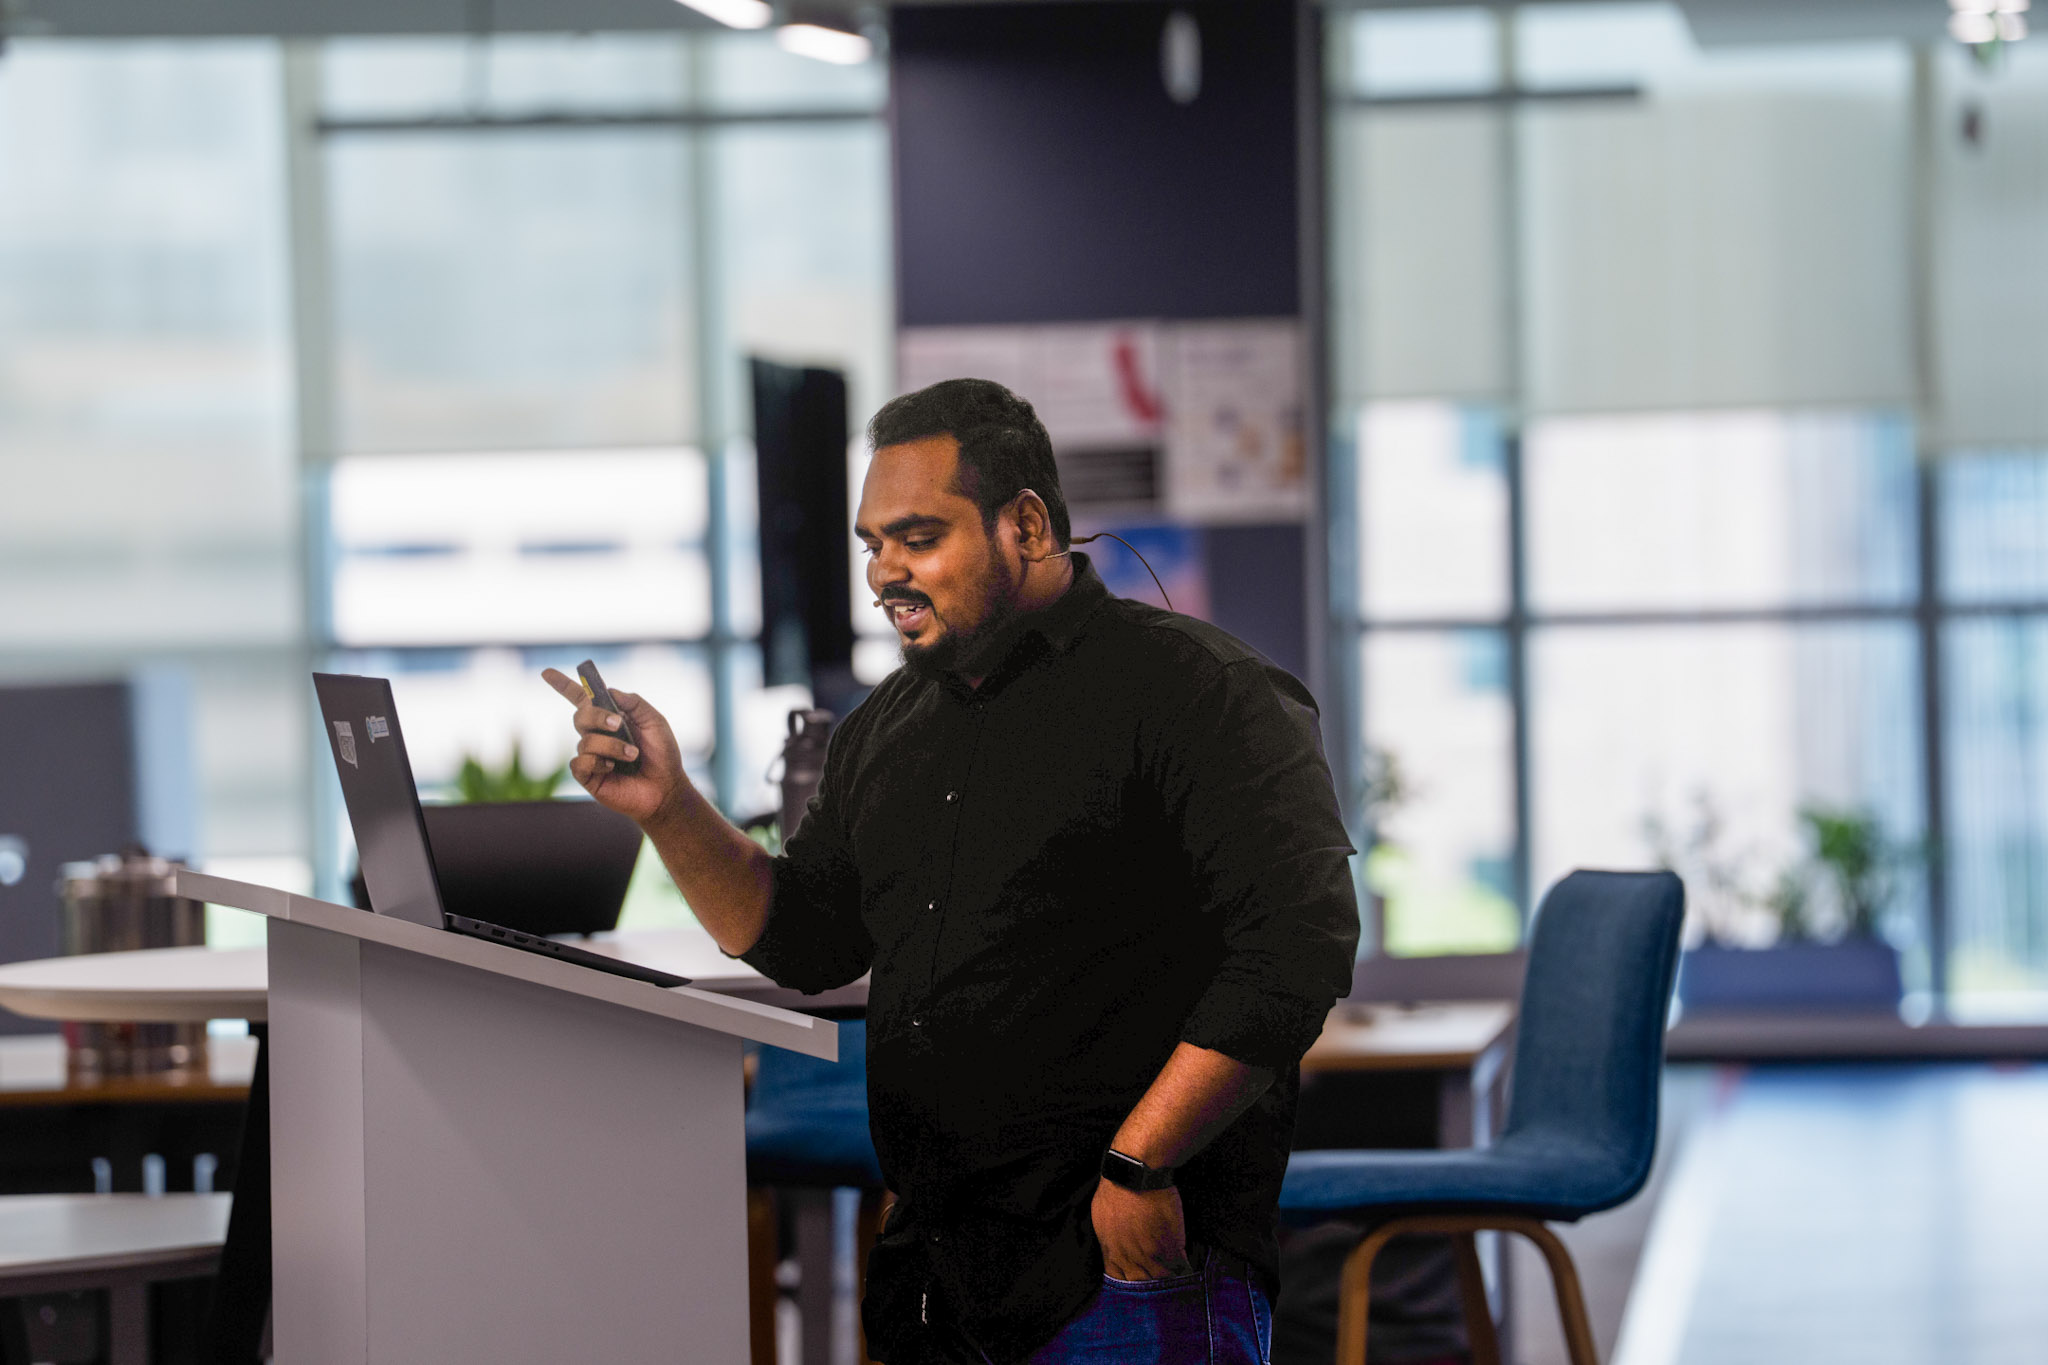
Chapter LeadershipI'm on the core team at null Hyderabad, India's community-driven infosec chapter. I help make sure events run smoothly end to end — reviewing speaker content, running the chapter's social media, and emceeing sessions on the day.
Meet the team →
Bug Bounty Brigade — Global Hacking Community
FounderA community of bug hunters, by bug hunters, for bug hunters — built around collaboration, knowledge sharing, and professional growth for security researchers, with a focus on responsible disclosure and ethical hacking practice.
Talk
null Hyderabad
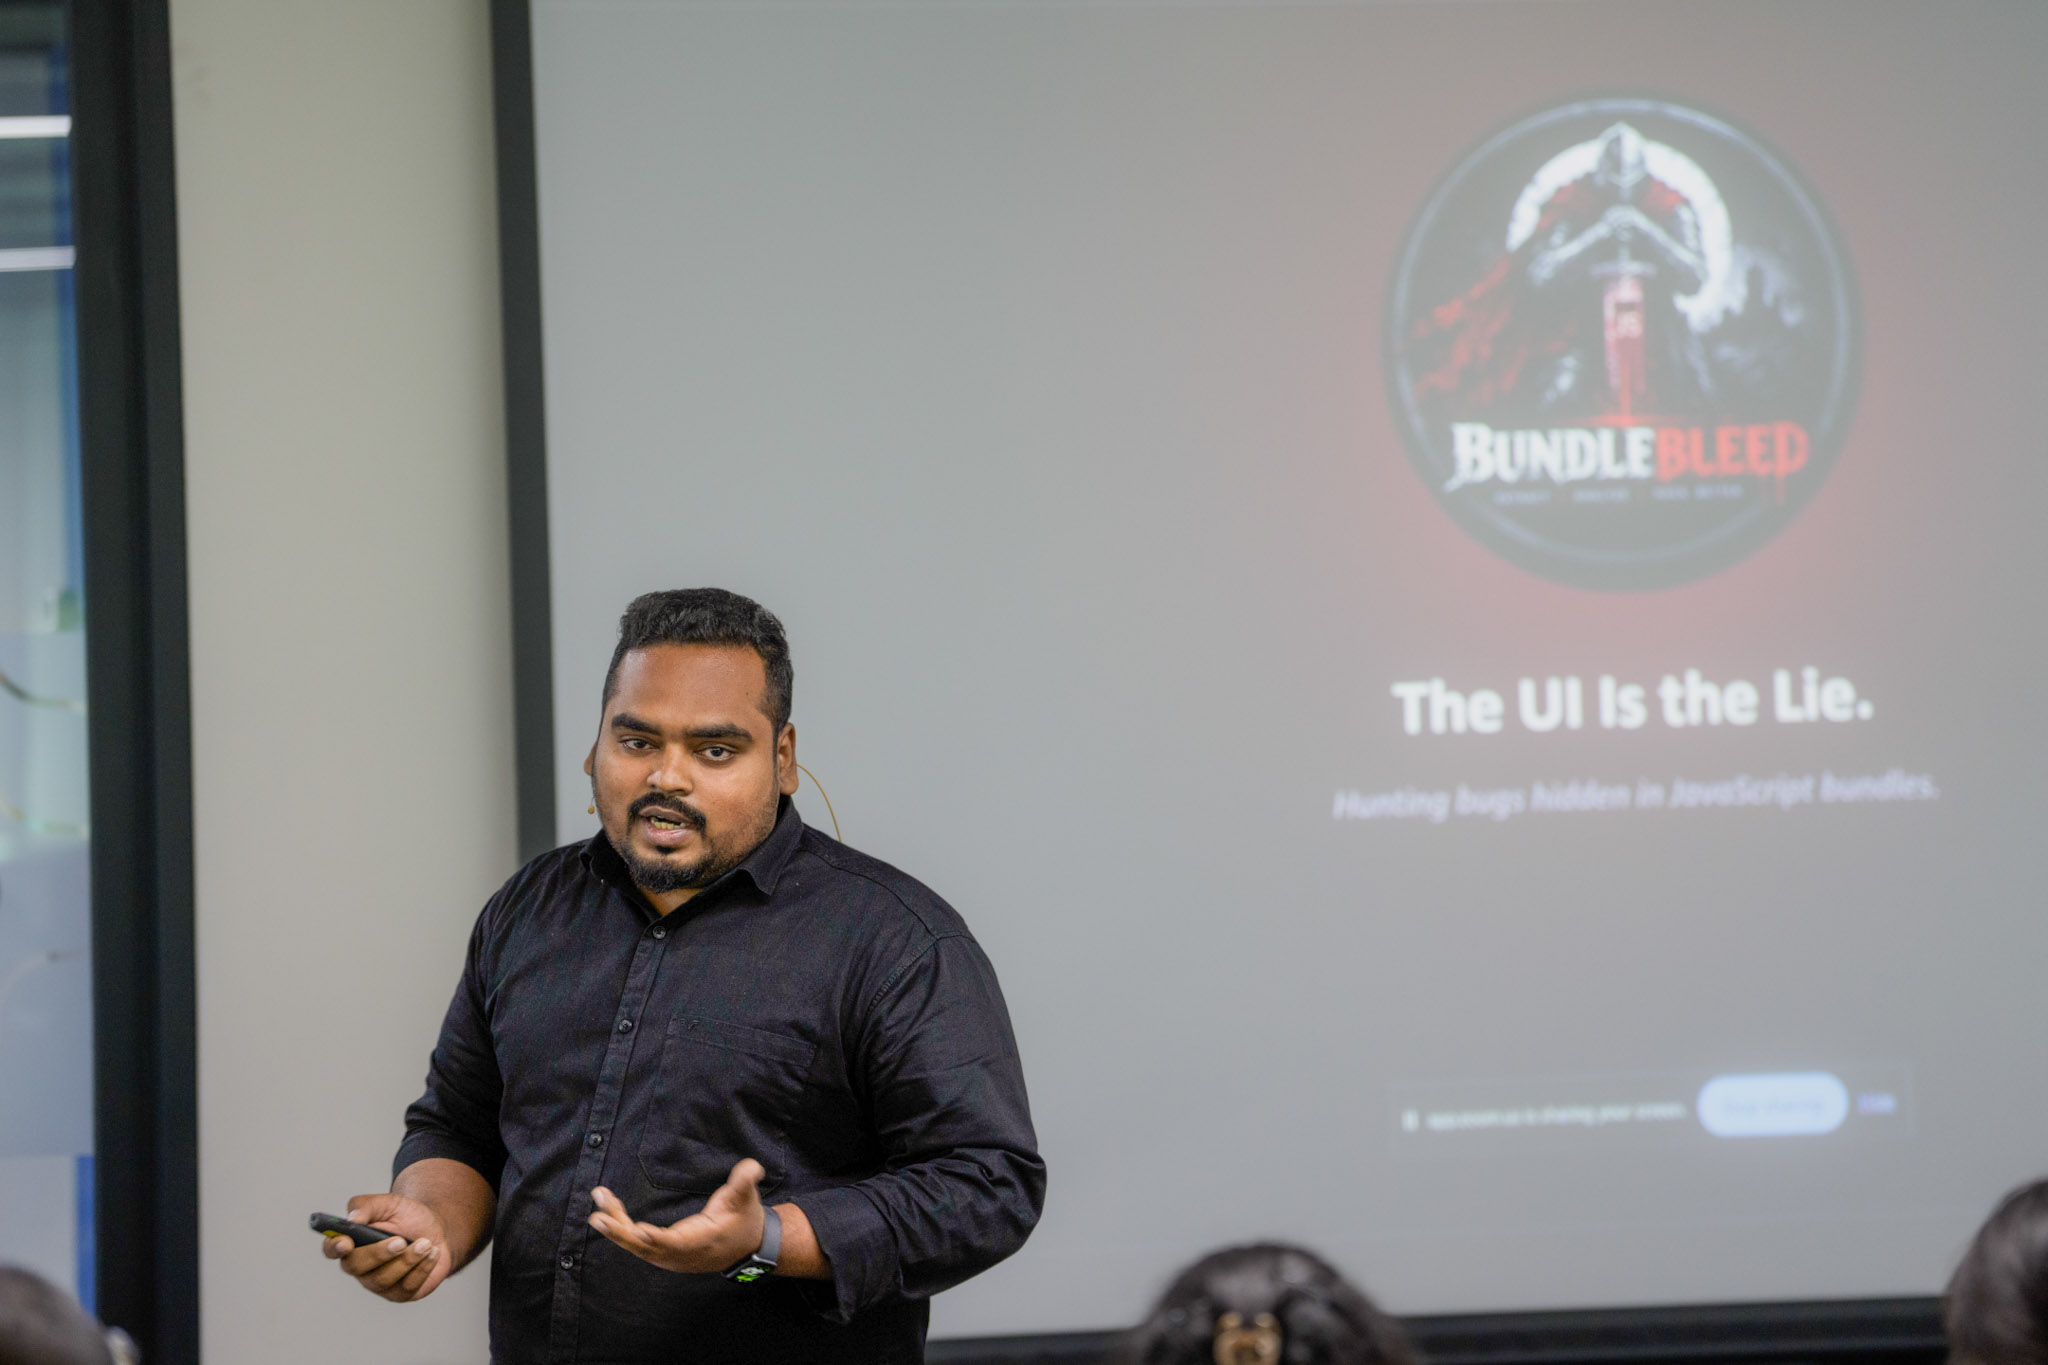
Why the rendered UI hides the real attack surface, and how to pull endpoints, secrets, and DOM-XSS-shaped sinks straight out of a target's JS bundles — the ideas that became BundleBleed.
View session on nullHyd →Featured build
Open-source AI attack surface management. Instead of another severity score, kiyooo puts every finding through evidence-cited LLM triage, with a human in the loop and local models by default — no hostname or finding leaves the network.
See how it works
Runtime behavioral security for AI agent skills. SkillFence watches what a skill actually causes an agent to do, scores capability drift, and pauses high-risk actions for a human before they execute.
Explore the project
AI/LLM-assisted JS recon and vulnerability triage for authorized bug bounty testing. Extracts endpoints, secrets, and DOM-XSS-shaped sinks from client-side JavaScript, then scores them into evidenced hypotheses — scope-gated, passive by default, and human-verified before anything sends.
Explore the project